✦
Demonstrate privacy accountability
Show customers and partners that privacy risks and responsibilities are managed systematically.
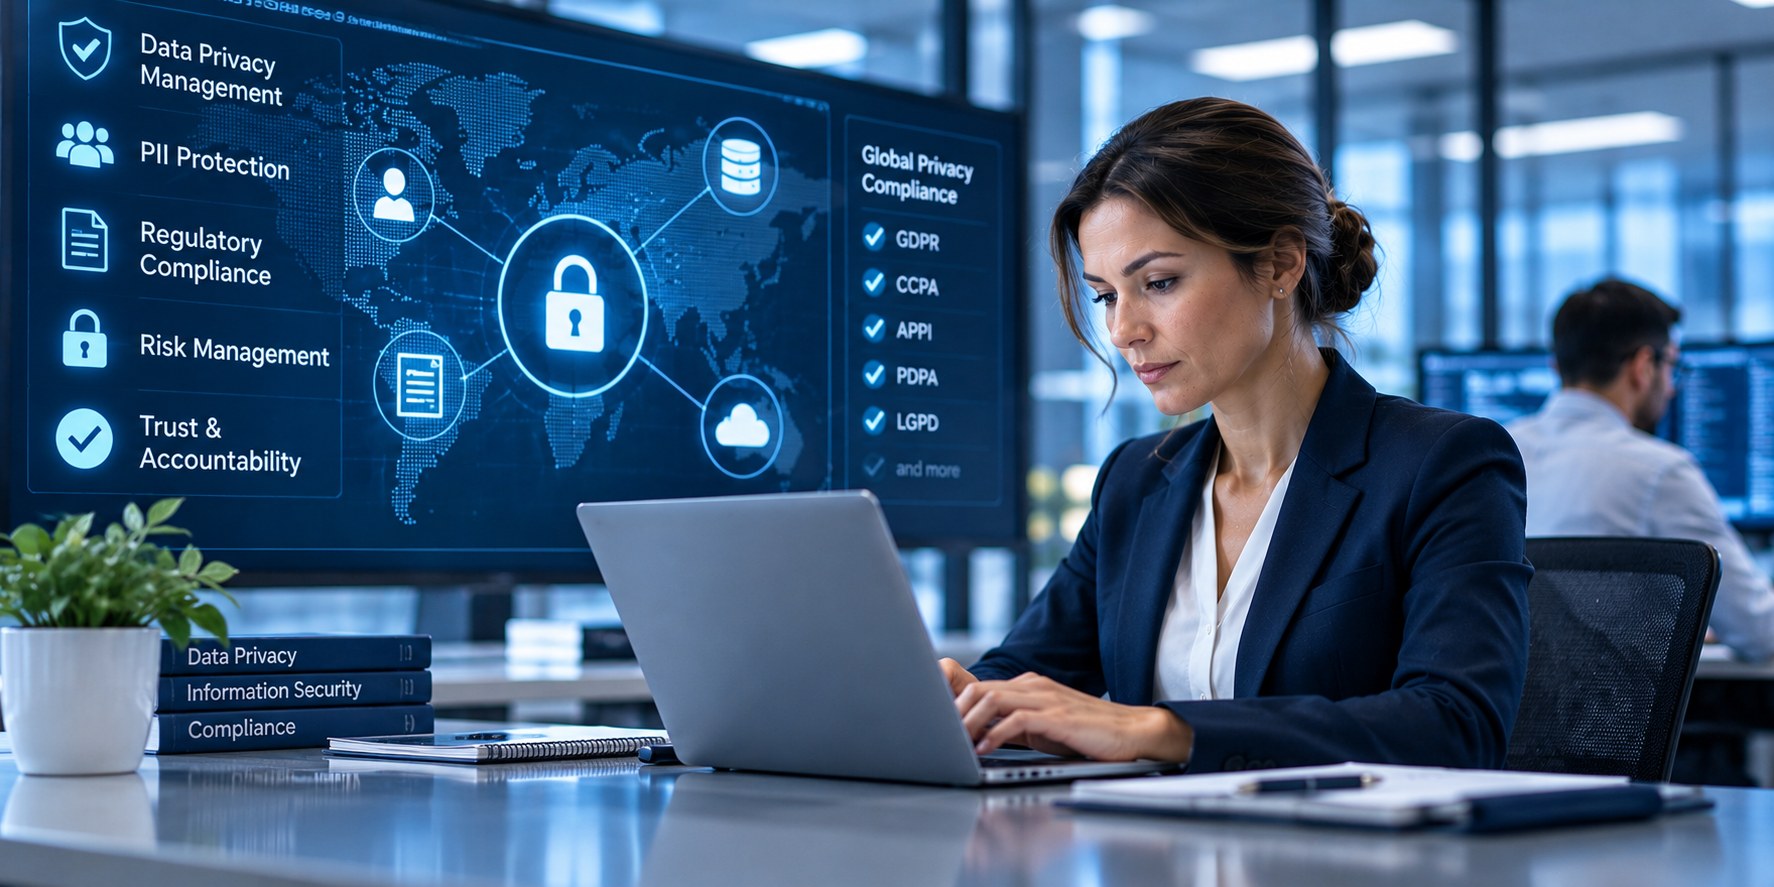
Demonstrate responsible handling of personal data with independent ISO/IEC 27701 certification audits for your privacy information management system.
Independent assessment of a structured approach to managing personal information and privacy risk.
Show customers and partners that privacy risks and responsibilities are managed systematically.
Provide independent assurance of the privacy information management system.
Establish controls appropriate to your role in handling personally identifiable information (PII).
Assess privacy risks, monitor controls and act on identified weaknesses.
Organise evidence and governance relevant to applicable privacy laws without claiming automatic legal compliance.
Coordinate privacy and information security systems where it benefits your organisation.
ISO/IEC 27701:2025 specifies requirements and provides guidance for a privacy information management system (PIMS). It is intended for organisations responsible for processing personally identifiable information (PII), including PII controllers and processors.
Important change: The 2025 edition is a standalone management system standard. Unlike the withdrawn 2019 edition, it does not require ISO/IEC 27001 certification as a prerequisite under the standard itself. It can still be integrated with an information security management system.
Certification is not a guarantee against breaches and does not replace privacy-law compliance obligations.
A structured audit pathway with a clear separation between coordination and independent certification decisions.
Tell us about the personal data you handle, your controller/processor roles, services and locations.
The certification body reviews the scope, applicable edition, accreditation status and audit programme.
Assess documented arrangements, scope, system readiness and preparation for the next audit.
Evaluate implemented privacy controls and management-system effectiveness through evidence and interviews.
The certification body reviews the audit results and makes the certification decision.
Scheduled surveillance and recertification audits help maintain confidence over the certification cycle.
Already certified under ISO/IEC 27701? Ask about transfer and transition arrangements. Eligibility depends on the certificate, existing accreditation, audit history, scope and the receiving certification body’s rules.
For certificates referencing the withdrawn 2019 edition, the applicable transition requirements should be confirmed before committing to a transfer date.
Blue Wolf coordinates independent certification services through certification-body relationships. The relevant certification body—not Blue Wolf—makes the certification decision and issues the certificate. Verify each body’s current ISO/IEC 27701:2025 accredited scope and standalone-certification availability before publication.
Certification enquiries, coordination and customer support.
Certification-body relationship; confirm ISO/IEC 27701:2025 scope.
Certification-body relationship; confirm ISO/IEC 27701:2025 scope.
Tell us about your organisation, privacy scope and locations. We’ll help you understand the available certification pathway.